On 27 June 2017 a cyberattack that began in Ukraine paralysed systems at Maersk, Mondelez, Merck and DLA Piper. How it differs from WannaCry and what a company should review.
On 27 June 2017 a malicious program known as NotPetya, a variant of the Petya family, spread through the networks of companies in several countries and paralysed their systems. The blow was felt first in Ukraine, where the central bank said several commercial banks and public and private companies had been attacked by an unknown virus, and then it reached companies in other countries.
Who has been affected
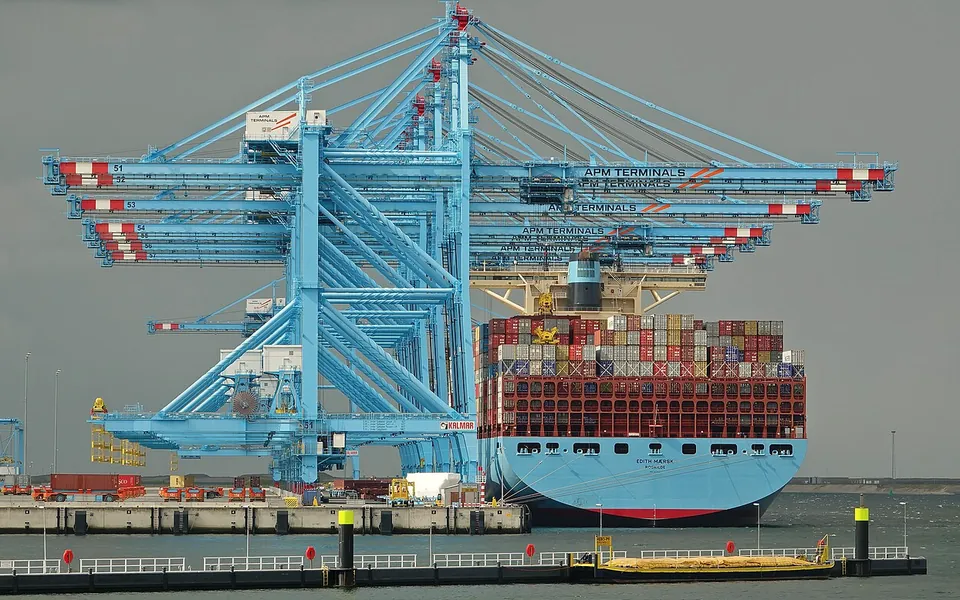
Among the victims that acknowledged it are the Danish shipping and port operator A. P. Moller-Maersk, which said its systems were down across several sites and business units, and whose port operator APM Terminals was also hit; the Russian oil company Rosneft, the pharmaceutical group Merck, the food maker Mondelez and the law firm DLA Piper. In Spain, the CCN-CERT, the response team of the National Cryptologic Centre, issued an alert, and Mondelez confirmed an incident in its information systems internationally.
How it works and how it differs from WannaCry
NotPetya encrypts the files on the machine and, if it gains administrator rights, the master boot record too, which leaves the computer unusable. The attackers demanded $300 in bitcoin, but the analysis reported by the United States Computer Emergency Readiness Team (US-CERT) indicates that paying probably does not work: the email address for contacting them was shut down by its provider and no link has been shown between the encryption key and the victim, so decryption may be impossible even if you pay. That is why it is described more as a destructive program than as ransomware.
It shares with WannaCry, the May attack, the same Windows flaw, known as EternalBlue, which Microsoft fixed with bulletin MS17-010 on 14 March 2017. But there are two differences. The first is the way in: WannaCry searched the network for machines with the SMBv1 file-sharing protocol accessible, whereas NotPetya was distributed through the Ukrainian tax accounting program M.E.Doc. The second is the spread: besides the flaw, NotPetya steals Windows credentials and uses them with legitimate administration tools, such as WMIC and PsExec, to jump from one machine to another, so applying the patch is not enough on its own.
What to review
The CCN-CERT advises updating the operating system and security software, keeping the firewall on, using secure protocols for remote administrator access, showing file extensions, disabling Office macros and not paying the ransom, because it does not guarantee decryption and only rewards the campaign. If there are no backups, it advises keeping the encrypted files before disinfecting the machine, in case a decryption tool appears in the future.
The US-CERT adds measures that this attack has made a priority: applying patch MS17-010 and disabling SMBv1, limiting administrator rights to the minimum necessary, restricting WMI and PsExec, splitting the network into segments so that an infected machine cannot reach all the others, and having an incident response and business continuity plan. Machines with M.E.Doc installed should be treated as suspect. In practice there are three concrete reviews: backups, which should exist, be kept outside the usual network so the virus does not encrypt them too, and have been tested by restoring them; who can log in with administrator rights and from where; and cyber insurance, what it covers (restoring systems, business interruption, data loss) and what the insurer requires.
For a company with suppliers or subsidiaries in several countries, the risk is not only its own: an attack at one site or at a supplier can reach all of them. It is worth knowing which third-party systems yours connect to and what happens to the business if one day there are no computers. Ask your adviser how it applies to your case.
NotPetya is a reminder that patching is not enough: business continuity depends on backups that work and on controlled access.
This article is general information. It is not legal, tax or investment advice, and it does not take anyone’s particular circumstances into account.