On 14 September 2019 Delegated Regulation (EU) 2018/389 starts to apply: strong authentication for electronic payments and online banking, with extra time for e-commerce.
On 14 September 2019 Delegated Regulation (EU) 2018/389 starts to apply. It is the technical standard under the second European payment services directive (PSD2) that sets out strong customer authentication (SCA). From that date, banks and other payment service providers must require it when the customer accesses their account online, initiates an electronic payment or carries out, through a remote channel, an action that may involve a risk of fraud. One of its aims is to reduce fraud in the authentication process.
What strong authentication requires
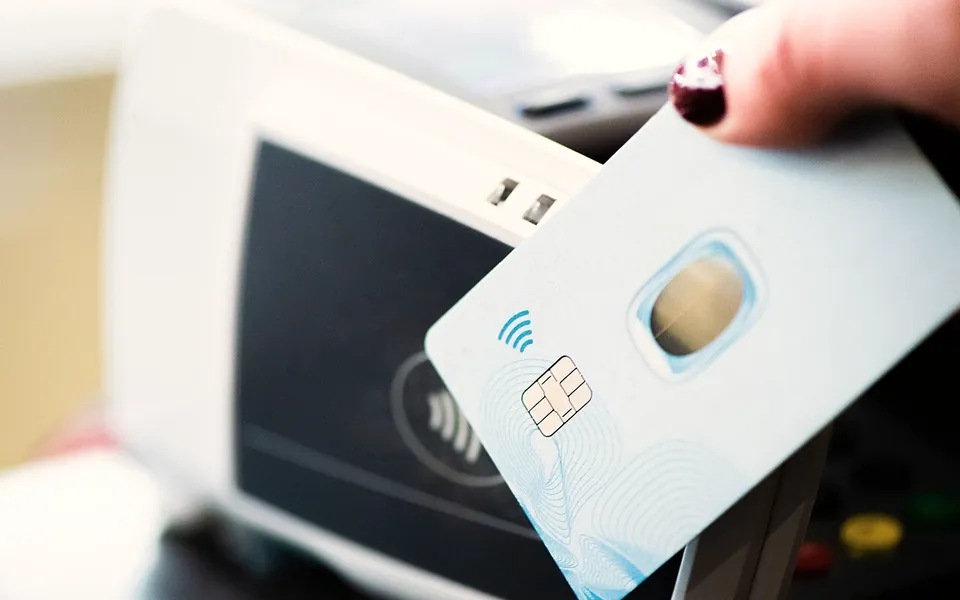
SCA means verifying the customer’s identity with two or more elements from three categories: something they know (a password or PIN), something they have (the phone or the card) and something they are (a fingerprint or other biometric data). The elements must be independent: a breach of one must not compromise the others.
The opinion of the European Banking Authority (EBA) of 21 June 2019 clarifies which methods qualify. Details printed on the card (number, expiry date and security code) count neither as knowledge nor as possession. An SMS code can qualify, but what is then being checked is possession of the phone, specifically the SIM card, not the message; and mobile apps can evidence possession if the device is bound to the customer.
Exemptions and extra time
The regulation provides for exemptions. They include contactless payments of up to €50 per transaction (with a cumulative cap of €150 or five transactions), remote payments of up to €30 (with a cumulative cap of €100 or five transactions) and viewing the balance and recent transactions, which does not require authentication each time provided it is done at least every 90 days. Trusted beneficiaries, recurring payments and a transaction risk analysis are also covered, with thresholds of €100, €250 and €500 depending on the provider’s fraud rate.
In addition, in that opinion the EBA acknowledges that some players in the payments chain, particularly online merchants, may not be ready on 14 September. It therefore accepts, on an exceptional basis, that national competent authorities may give payment service providers limited extra time to migrate, on one condition: that they have a migration plan agreed with their authority and carry it out urgently. The EBA stresses that it cannot move the application date, which is set in EU law, and that it will announce later in 2019 the deadlines for completing the migration.
What changes for users
For customers, the change shows up as extra steps when logging in to online banking and paying online: a password or PIN plus a code sent to the phone, a banking app or a fingerprint. During the migration period some card purchases may still be processed under the old system, provided the institution has its plan agreed with the Bank of Spain, which said on 11 September that it will review them.
It is worth checking that the bank has your current mobile number and that the app or verification device is activated, because without them a payment or login could be rejected. Codes and passwords are not to be given to third parties, not even to someone claiming to be a bank employee. Companies that take payments online should ask their payment provider about its migration plan. Ask your bank how it applies to your accounts and cards.
The security of a payment no longer rests on a single piece of data, but on the combination of two.
This article is general information. It is not legal, tax or investment advice, and it does not take anyone’s particular circumstances into account.