On 17 March 2018 it emerged that Cambridge Analytica had obtained data on more than 50 million Facebook users. What is known as of 22 March, and what the European regulation, applicable from 25 May, will demand of companies.
On 17 March 2018 The Observer and The New York Times reported, with testimony from Christopher Wylie, a former employee of the firm, that the British political analytics company Cambridge Analytica had obtained data on more than 50 million Facebook users without their permission. The day before, Facebook had announced that it was suspending the firm and its parent, SCL (Strategic Communication Laboratories), as well as Wylie and the academic Aleksandr Kogan.
What is known
According to Facebook, Aleksandr Kogan, a psychology professor at the University of Cambridge, created a personality-quiz app that used Facebook Login and was downloaded by about 270,000 people. Those users gave permission to share their profile data and, in part, that of their friends where their privacy settings allowed it. Kogan later passed that data to SCL and Cambridge Analytica, which, according to Facebook, broke its rules. The social network says it learned of this in 2015, removed the app and demanded certification that the data had been deleted, and that a few days ago it received reports that not all of it had been.
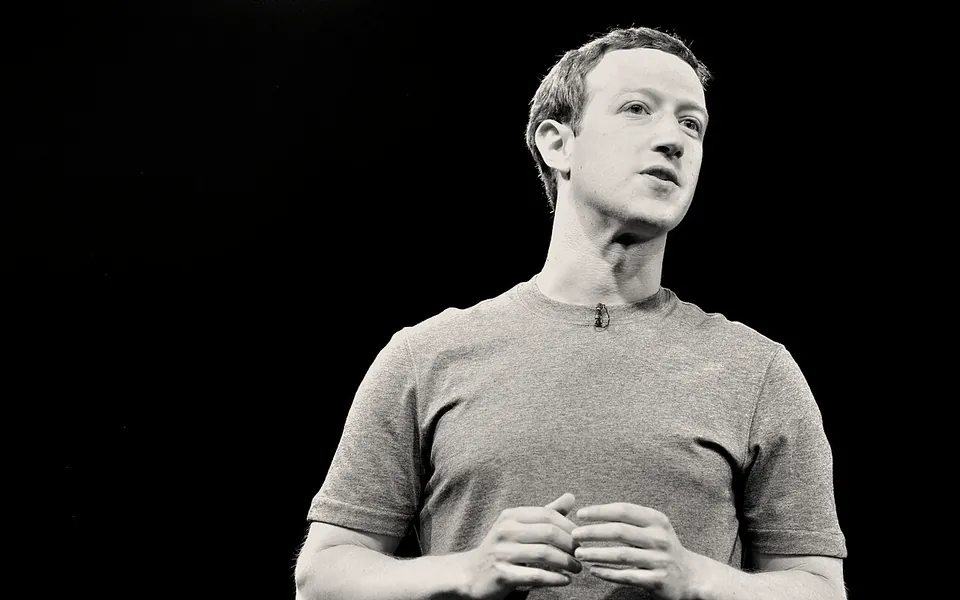
Facebook rejects the idea that this was a data breach: it says users signed up voluntarily and that its systems were not infiltrated and no passwords were stolen. On 21 March Mark Zuckerberg broke his silence with a message in which he acknowledged a breach of trust between Facebook and the people who share their data with it, apologised and announced measures: auditing apps that accessed a lot of data before 2014, limiting what developers can obtain and notifying affected users.
The reaction
On the stock market, Facebook closed on Monday 19 March down 6.8% and fell again on Tuesday; CNBC put the value lost since Monday at almost $50 billion. Bloomberg reported on 20 March that the US Federal Trade Commission (FTC) is examining whether Facebook breached its 2011 agreement to obtain users’ consent before changing their privacy settings; the FTC said it could not confirm whether it is investigating, and Facebook denies having breached that agreement. Several senators, and also British and European legislators, have demanded that Zuckerberg appear.
In the United Kingdom, the Information Commissioner, Elizabeth Denham, who heads the Information Commissioner’s Office (ICO), the data protection regulator, said she will seek a court warrant to obtain information and access to Cambridge Analytica’s systems, because it did not respond by the deadline to the demand she made on 7 March. She also asked Facebook to stop its audit at the firm’s offices, because it could compromise an investigation. The inquiry covers the acquisition and use of Facebook data by SCL, Kogan and Cambridge Analytica.
What the European regulation changes
The General Data Protection Regulation (GDPR), Regulation (EU) 2016/679, will apply from 25 May 2018. It also applies to companies not established in the European Union that process data of people who live there in order to offer them goods or services or to monitor their behaviour. Where processing is based on consent, the controller must be able to demonstrate that it was given.
Security breaches must be notified to the supervisory authority without undue delay and, where feasible, within 72 hours. And fines for infringing the basic principles of processing, including the conditions for consent, can reach €20 million or 4% of annual worldwide turnover, whichever is higher. It does not apply yet: the case is being examined under the rules in force today, which the regulation will replace.
If your company handles data on customers, employees or suppliers, it makes sense to start with an inventory: what data it collects, for what purpose and on what legal basis. Where the basis is consent, check that it was requested specifically, that it can be demonstrated and that whoever gave it can withdraw it at any time.
It is also worth reviewing the chain of third parties. In this case the problem was not only who collected the data but to whom it was passed on afterwards. Every company that hands data to a marketing agency, an analytics provider or an app should be able to answer what data it hands over, under what contract and what happens if the recipient passes it on to others. And there should be a procedure to detect an incident and report it within 72 hours.
Customer data is an asset and also a responsibility: from 25 May, the law will demand it, with fines attached.
This article is general information. It is not legal, tax or investment advice, and it does not take anyone’s particular circumstances into account.